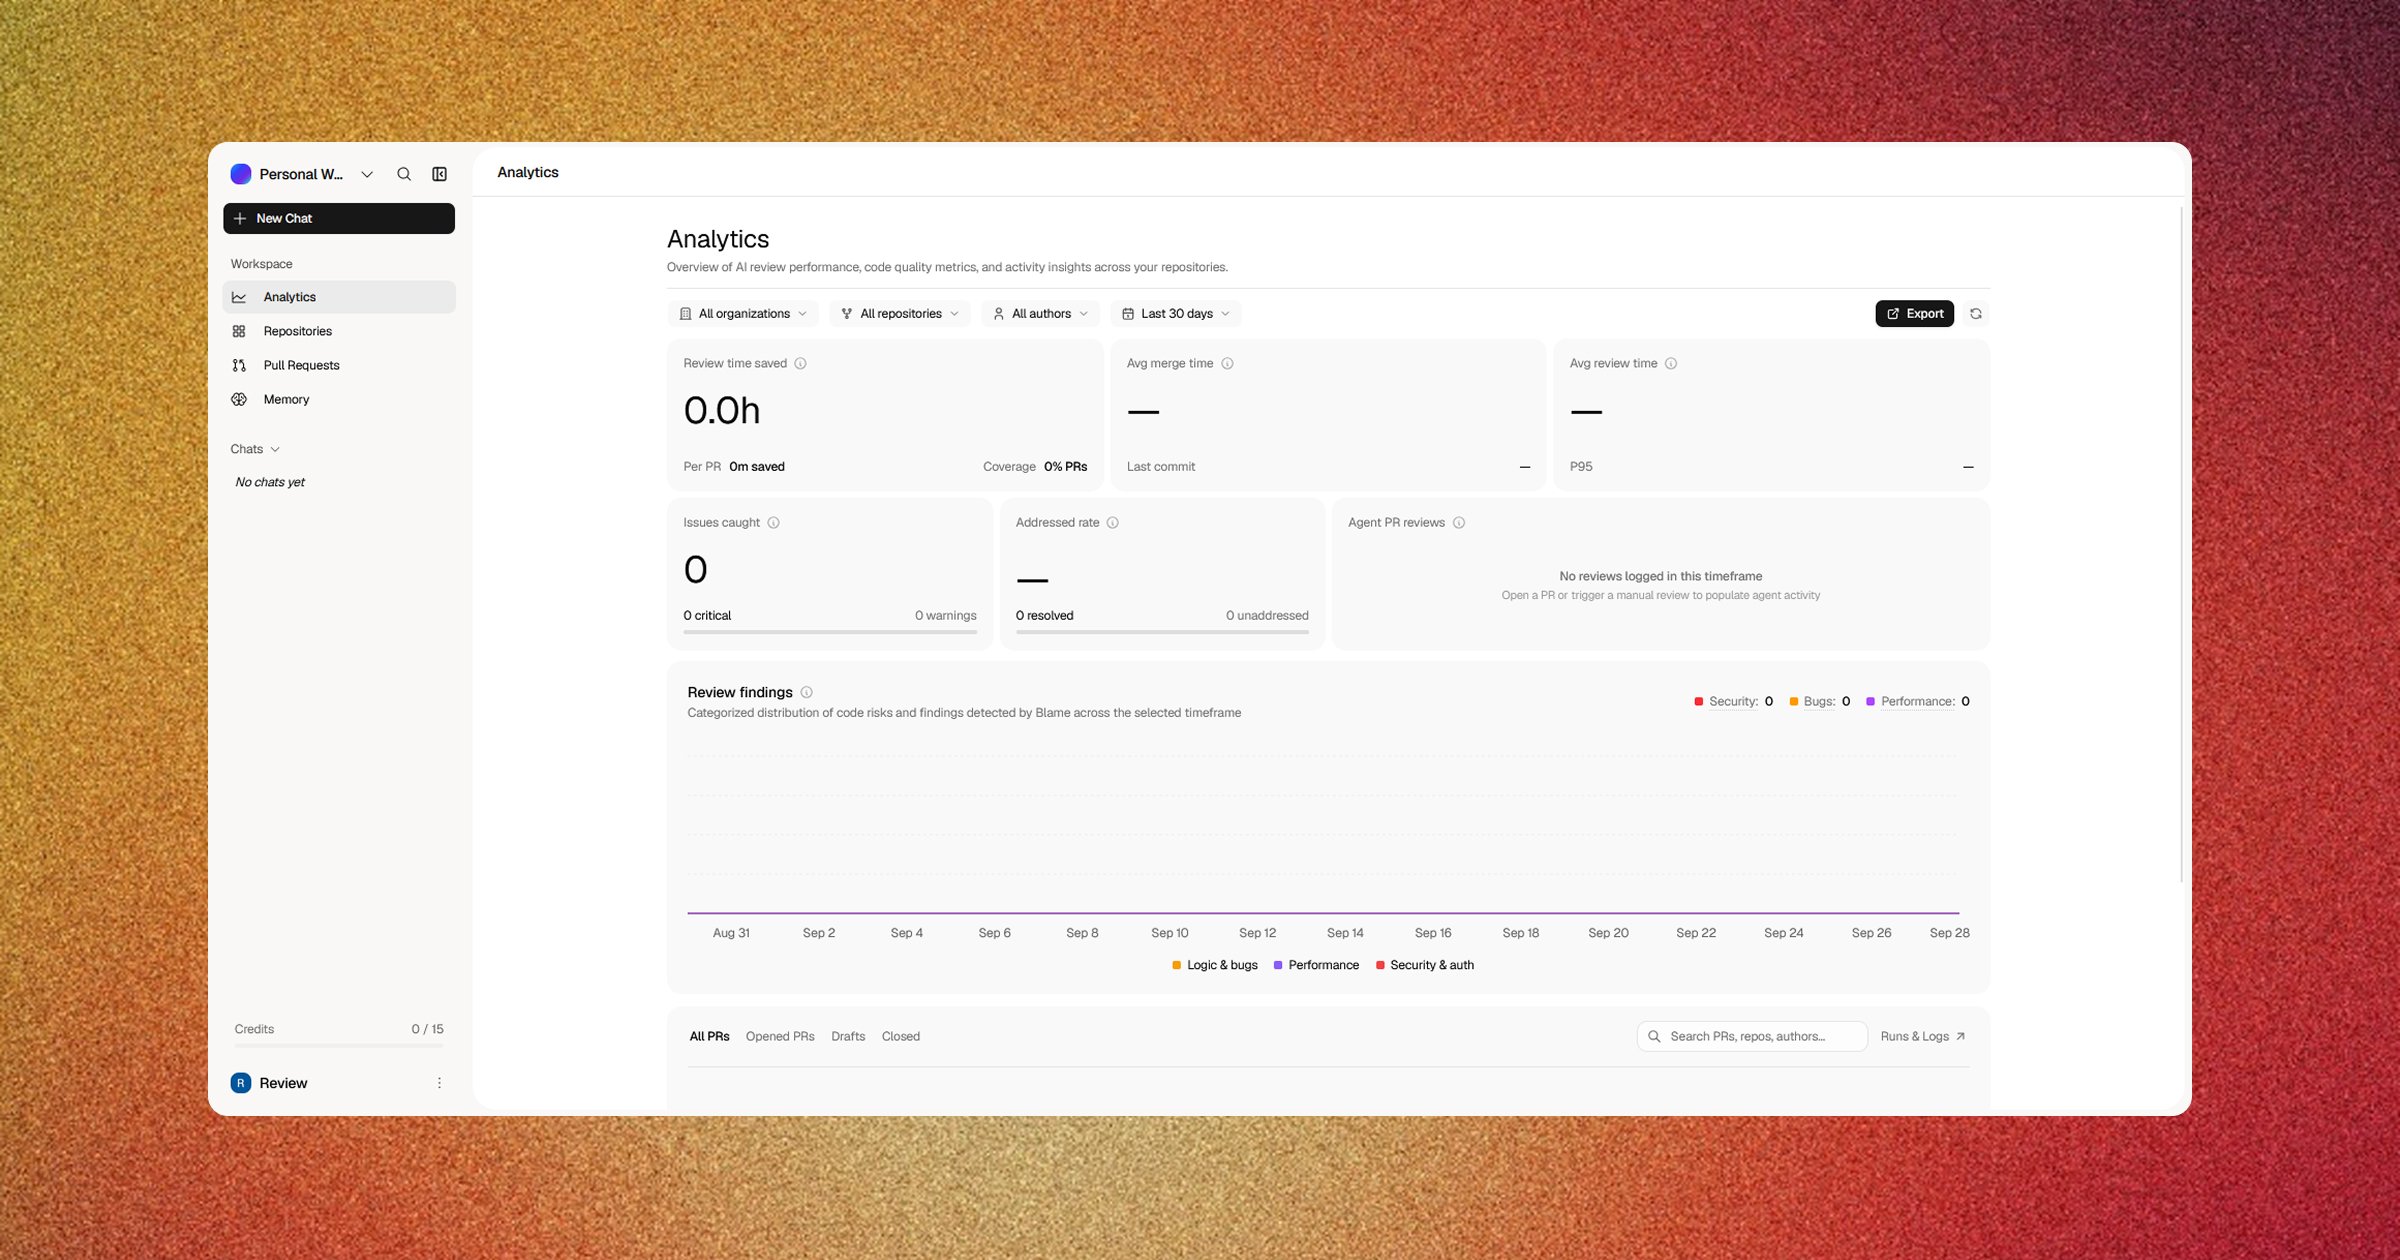
The Analytics dashboard provides engineering leaders and teams with end-to-end visibility into code review turnaround, defect prevention, and AI review efficacy. Access it anytime directly from the main workspace navigation under Analytics.
Filters & Scoping
Use the top filter bar to drill down into specific teams, projects, or development cycles.
Export Data: Click the Export button in the filter bar to download the scoped analytics dataset as a timestamped .json file (blame-analytics-{range}-{date}.json) for external reporting or BI pipelines.
KPI Summary Cards
The top of the dashboard highlights core efficiency, velocity, and code quality indicators:
Trend Charts & Findings Breakdown
The interactive Review Findings chart tracks issue velocity and category distribution across your chosen timeframe:
Finding Categories
- Security & Auth: Injection vulnerabilities (SQLi, XSS), exposed secrets/API keys, authentication flaws, OWASP Top 10 vulnerabilities, and unsafe dependencies.
- Logic & Bugs: Runtime exceptions, unhandled
null/undefined states, race conditions, broken control flow, and code quality antipatterns.
- Performance: N+1 database queries, unindexed lookups, memory leaks, unoptimized React re-renders, and inefficient algorithmic complexity.
Pull Request Inspection & Actions
Below the charts, the Pull Requests Feed lists all scoped PRs with rich status indicators:
- Tab Filters: Filter between
All, Open, Draft, and Closed / Merged PRs.
- Review Badges: Real-time evaluation status (
PASSED, WARNING, FAILED).
- Issue Counts: Number of critical bugs and warnings detected per pull request.
- Inline Actions: Trigger manual reviews on-demand, convert open PRs to draft mode, or mark drafts as ready directly from the table.
Using Analytics to Improve Code Quality
If authors are not resolving review comments, your repository guidelines may be too noisy or pedantic. Consider adjusting custom repository rules under Repository Settings → Rules or lowering nitpick strictness.
A sudden spike in security findings usually indicates newly introduced libraries or auth changes. Inspect the affected repository from the leaderboard and review recent dependency updates.
If Blame reviews complete in < 1m but PRs take days to merge, the bottleneck is human review turnaround or CI pipeline queue times. Use this data to streamline approval policies.