> ## Documentation Index
> Fetch the complete documentation index at: https://docs.getblame.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Auto-Approve Low-Risk PRs
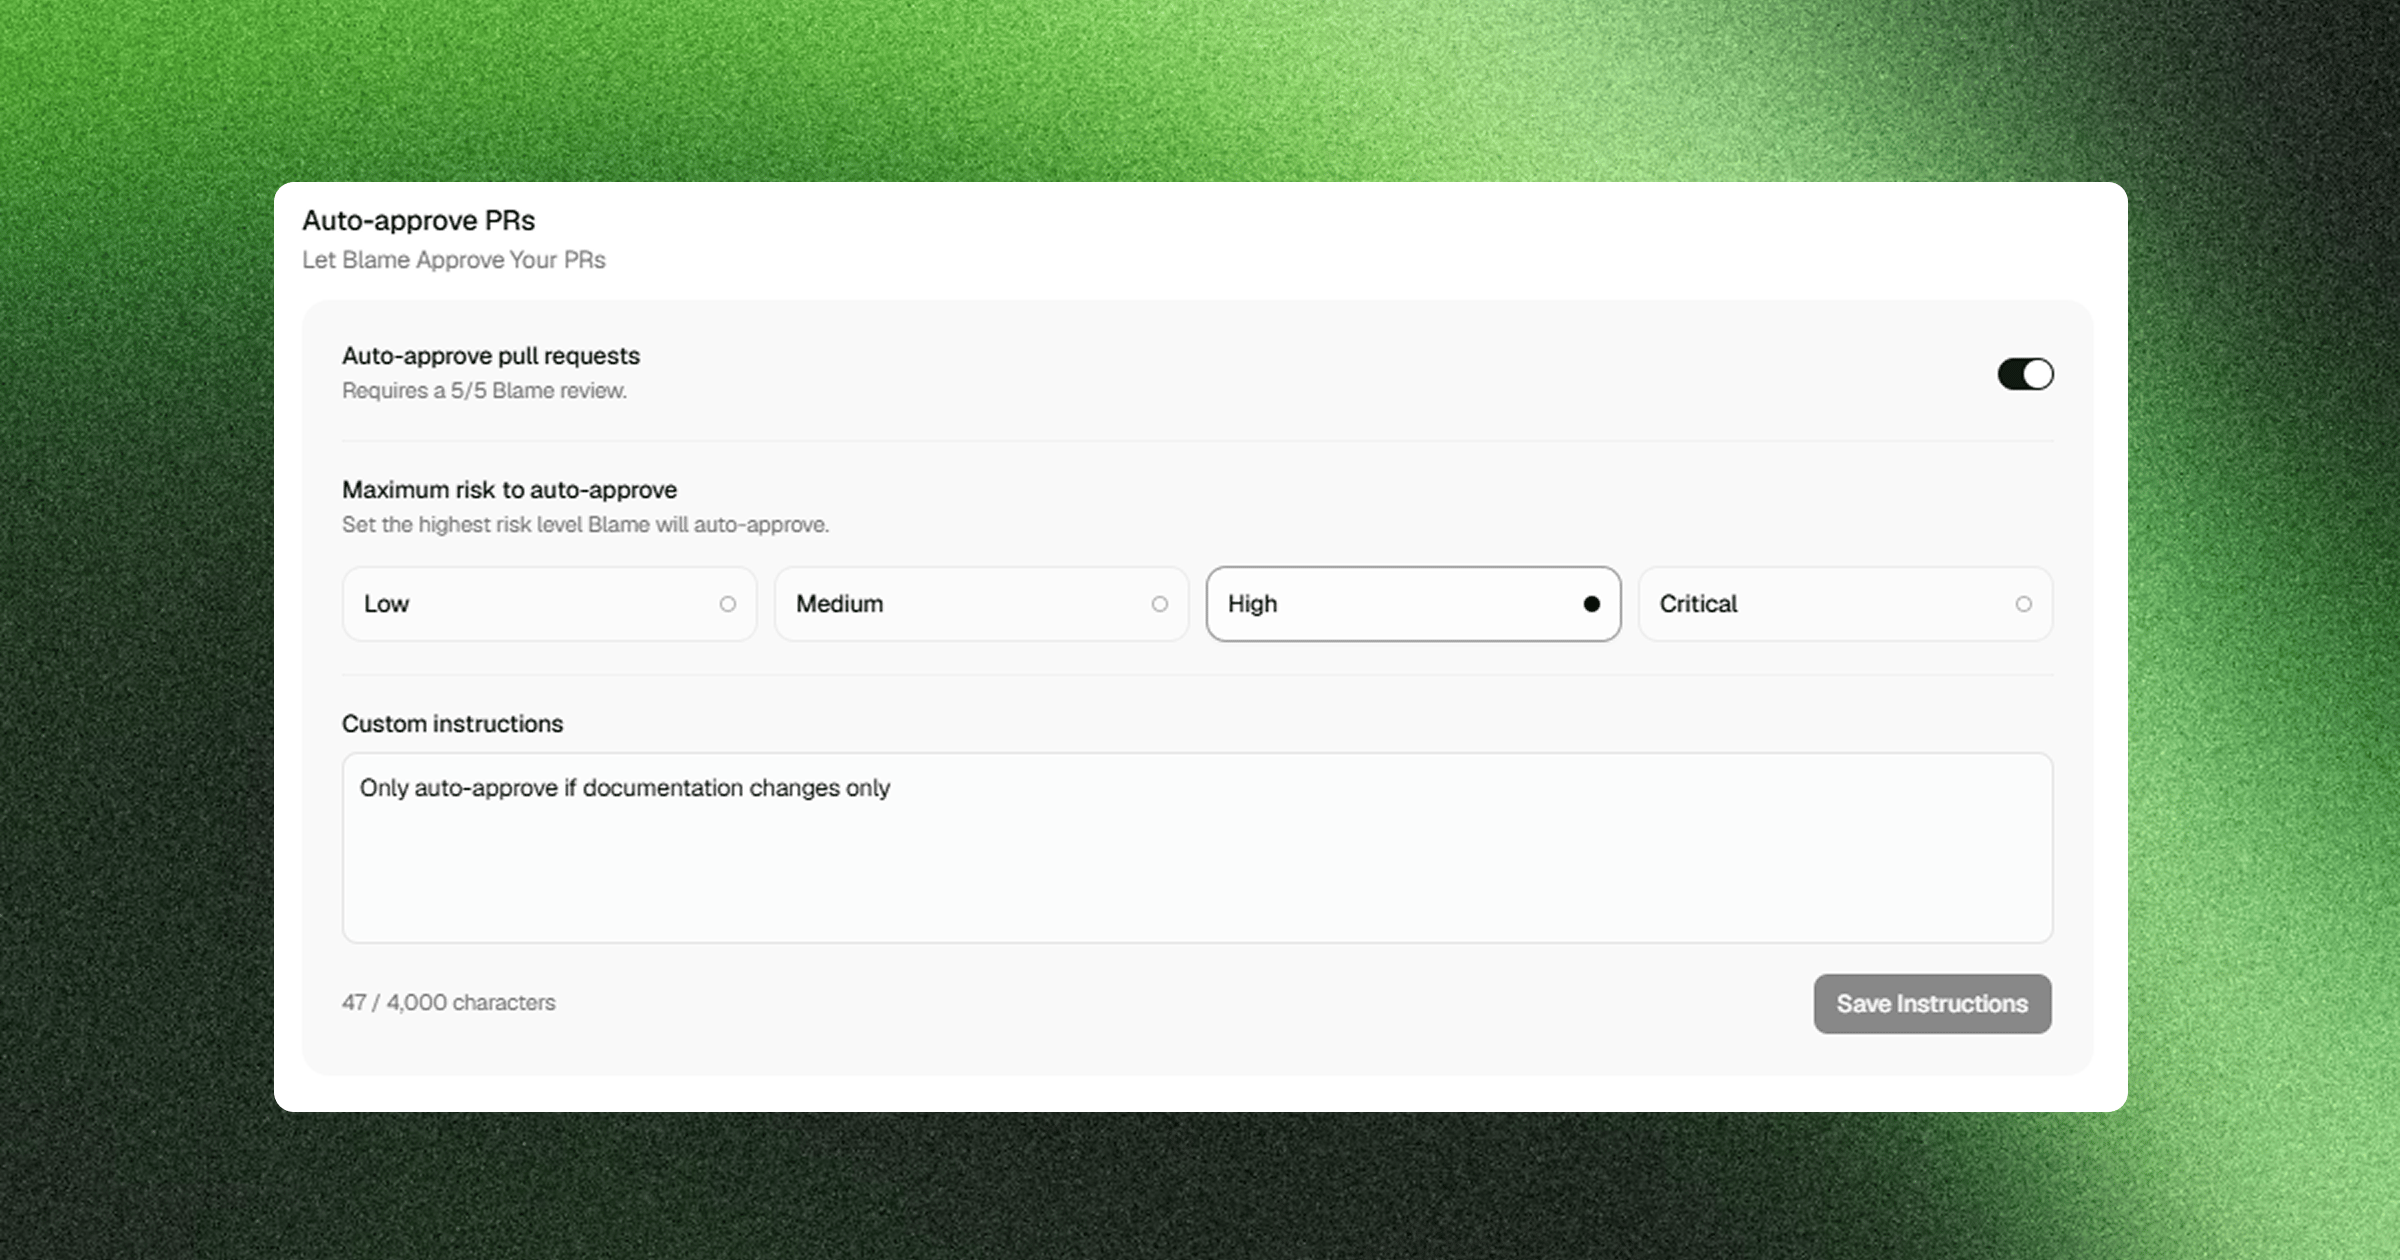
Reviewing routine, mechanical, or documentation pull requests consumes valuable engineering hours. Blame’s **Auto-Approve** feature allows teams to automatically submit an approving review on GitHub for pull requests that meet strict safety, quality, and risk criteria.
 ***
## How Auto-Approve Works
When a pull request is created or updated, Blame runs its full GraphRAG evaluation pipeline. If the pull request meets all the following conditions, Blame automatically submits an `APPROVE` review via the GitHub App:
1. **Flawless Review Rating**: The review achieves a `5/5 Confidence Score` (`Production ready`) with zero critical or high-severity findings.
2. **Within Maximum Risk Cap**: The assessed risk profile of the changes does not exceed your configured risk threshold.
3. **Satisfies Approval Guidelines**: The diff complies with your team's natural-language auto-approval instructions.
```mermaid theme={null}
flowchart TD
PR[Pull Request Analyzed] --> ConfScore{Score == 5/5 & 0 Defects?}
ConfScore -- No --> NormalReview[Post Standard Review Comments & Summary]
ConfScore -- Yes --> RiskCheck{Assessed Risk <= Max Risk Cap?}
RiskCheck -- No --> NormalReview
RiskCheck -- Yes --> GuidelineCheck{Satisfies Custom Instructions?}
GuidelineCheck -- No --> NormalReview
GuidelineCheck -- Yes --> SubmitApproval[Submit GitHub Review: APPROVE]
SubmitApproval --> UnblockMerge[Pull Request Approved & Unblocked]
```
***
## Configuring Auto-Approve in Blame
Auto-approve settings can be configured per repository or organization-wide in **Settings > Code Review**:
### 1. Enable Auto-Approve (`auto_approve_prs`)
* **Enabled**: Blame evaluates eligible PRs for automatic approval.
* **Disabled (Default)**: Blame only posts informational reviews and check runs without issuing approvals.
### 2. Maximum Risk Level (`auto_approve_max_risk`)
Set the ceiling for what level of risk Blame is permitted to approve automatically:
| **Risk Level** | **Suitable Change Types** | **Example Scenarios** |
| :- | :- | :- |
| `Low` *(Recommended)* | Purely non-breaking, superficial, or self-contained changes. | Markdown docs, typos, test additions, translation files, SVG asset updates. |
| `Medium` | Standard isolated feature enhancements with full test coverage. | Internal utility helper additions, isolated UI styling tweaks, dependency patches. |
| `High` | Broad architectural modifications. | Database schema migrations, core auth modifications, public API contract refactors. |
| `Critical` | Unrestricted approval (All risk tiers). | *Not recommended for production environments.* |
***
## Custom Approval Instructions
To ensure Blame approves only specific categories of pull requests, you can define natural-language rules in the **Custom instructions** field (up to 4,000 characters).
### Recommended Instruction Templates
#### Scenario A: Documentation & Test Additions Only
```markdown theme={null}
Only auto-approve if the diff is restricted to:
1. Markdown files (`.md`, `.mdx`), documentation folders (`docs/**`), or repository READMEs.
2. Test files (`*.test.ts`, `*.spec.ts`, `tests/**`) with no modifications to source logic.
Do NOT auto-approve if any file in `src/`, `lib/`, or package manifests is modified.
```
#### Scenario B: Dependency & Automated Bot Updates
```markdown theme={null}
Auto-approve dependency bump PRs (e.g. from Dependabot or Renovate) only if:
- All CI test suites pass.
- No breaking major version changes are introduced.
- No public API signatures are modified.
```
#### Scenario C: Isolated Frontend Styling & Content
```markdown theme={null}
Allow auto-approval for CSS, Tailwind classes, and static copy updates in `app/(marketing)/**`.
Never auto-approve modifications in `backend/`, `api/`, or authentication middleware.
```
***
## Safety Controls & Guardrails
To protect against unintended approvals:
* **Draft PR Exclusions**: Auto-approve evaluates pull requests only when they are marked **Ready for review** (unless draft reviews are explicitly enabled).
* **Branch Protection Compliance**: When combined with **GitHub Status Checks**, a PR will still require all required CI workflows and status checks to pass before merging.
* **Immediate Invalidation on New Commits**: If a developer pushes new commits to an approved PR, Blame re-evaluates the entire diff and invalidates the previous approval if new issues or risks are introduced.
***
## Related Documentation
* [**CI/CD Quality Gates & Status Checks**](/git-hub-status-checks) — Enforcing status check rules on pull requests.
* [**Configuring Review Strictness & Customization**](/review-strictness-and-customization) — Calibrating review depth and comment visibility.
* [**Review Architecture & Anatomy**](/review-architecture) — Complete anatomy of Blame review comments.